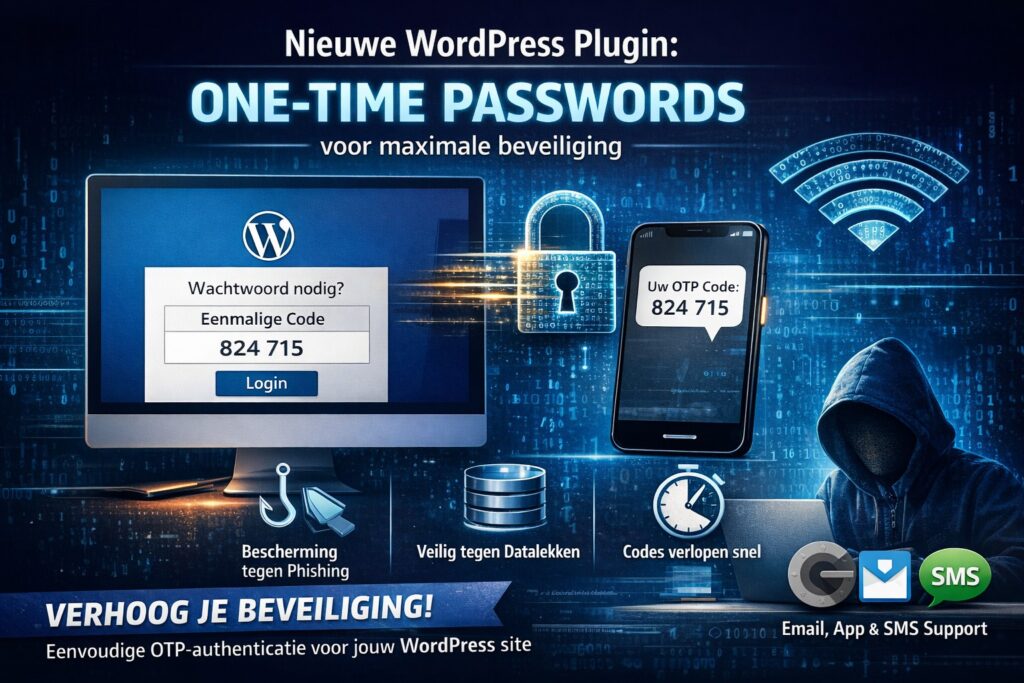
We are launching a new WordPress plugin that generates One-Time Passwords (OTP). Minor news? Absolutely not — this is one of the most impactful security steps you can take for your WordPress site today.
Why ordinary passwords are no longer enough
A traditional password is static. Created once, reused time and again. If it is intercepted — through phishing, a data breach or brute force — an attacker has unlimited access. As long as the password is not changed, the risk remains.
An OTP solves this structurally. Every login attempt generates a unique, time-limited code. Stolen? Useless. Intercepted? Too late. It is a simple principle with an enormous effect.
How does the plugin work?
- The user logs in — When logging in or performing a sensitive action such as a password reset, an OTP is generated automatically.
- Code delivered by email or SMS — The code is sent immediately to the user’s registered email address or phone number.
- The user enters the code — The code is valid for 5 minutes and can only be used once. Once entered, it becomes permanently unusable.
- Rate limiting protects against brute force — After three failed attempts, the account is temporarily locked. Advanced attacks don’t stand a chance.
Download the plugin here: [wpdm_package id=’4807′]
Why this is an important step
At Kyzoe we host more than 10,000 websites. Every day we see what can go wrong when security is treated as an afterthought. A hacked WordPress site doesn’t just cost you data — it costs you your reputation, customers and time.
OTP authentication is the most accessible form of two-factor authentication. No separate app, no hardware token — just a code in your inbox. Anyone can use it, and yet it drastically increases your security.
A stolen OTP is worthless. Even if an attacker intercepts the code in transit, it will already have expired or been used by the time they try it. That is the power of single use.
The plugin works out of the box on any standard WordPress installation and requires no technical knowledge to set up. Install, activate, secured.
Ready to secure your WordPress site better? Contact our team for more information or a demo.
Read also
WordPress 7.2 turns on the /random/ URL by default on December 8
WordPress 7.2 adds a /random/ URL that redirects visitors to a random post, and it is on by default. Who should check…
Read moreBlack Friday: how to get your website ready for the rush
On Black Friday your website gets far more visitors in a short time. With caching, lighter pages and a tested checkout you…
Read more
Novamira: an AI agent working directly in your WordPress site
With Novamira, an AI agent such as Claude or Cursor works directly in WordPress. What it can do, what Pro adds, how…
Read more